CPTS earned · 21 Oct 2026

Offensive security · Vulnerability research

Gabriel GomesAlmeida.

CPTS-certified penetration tester. Security researcher.

Two CVEs published in open source applications. Development and automation experience to understand code, investigate vulnerabilities, and communicate fixes.

02. Published CVEs
CPTS Certified by HTB
Dev + Sec Code and security

Open to opportunities · Brazil · Remote

01 / Certifications and education

CPTS. An achievement you can verify.

Passed the Hack The Box certification exam. A practical foundation for investigating, documenting, and communicating security risks.

CPTS badge — Hack The Box Certified Penetration Testing Specialist
Hack The Box

Certified Penetration Testing Specialist

Pentest methodology, enumeration, web security, Active Directory, pivoting, and technical reporting. Certification earned on 21 October 2026.

Passed · 21 Oct 2026
Web SecurityActive DirectoryPenetration Testing
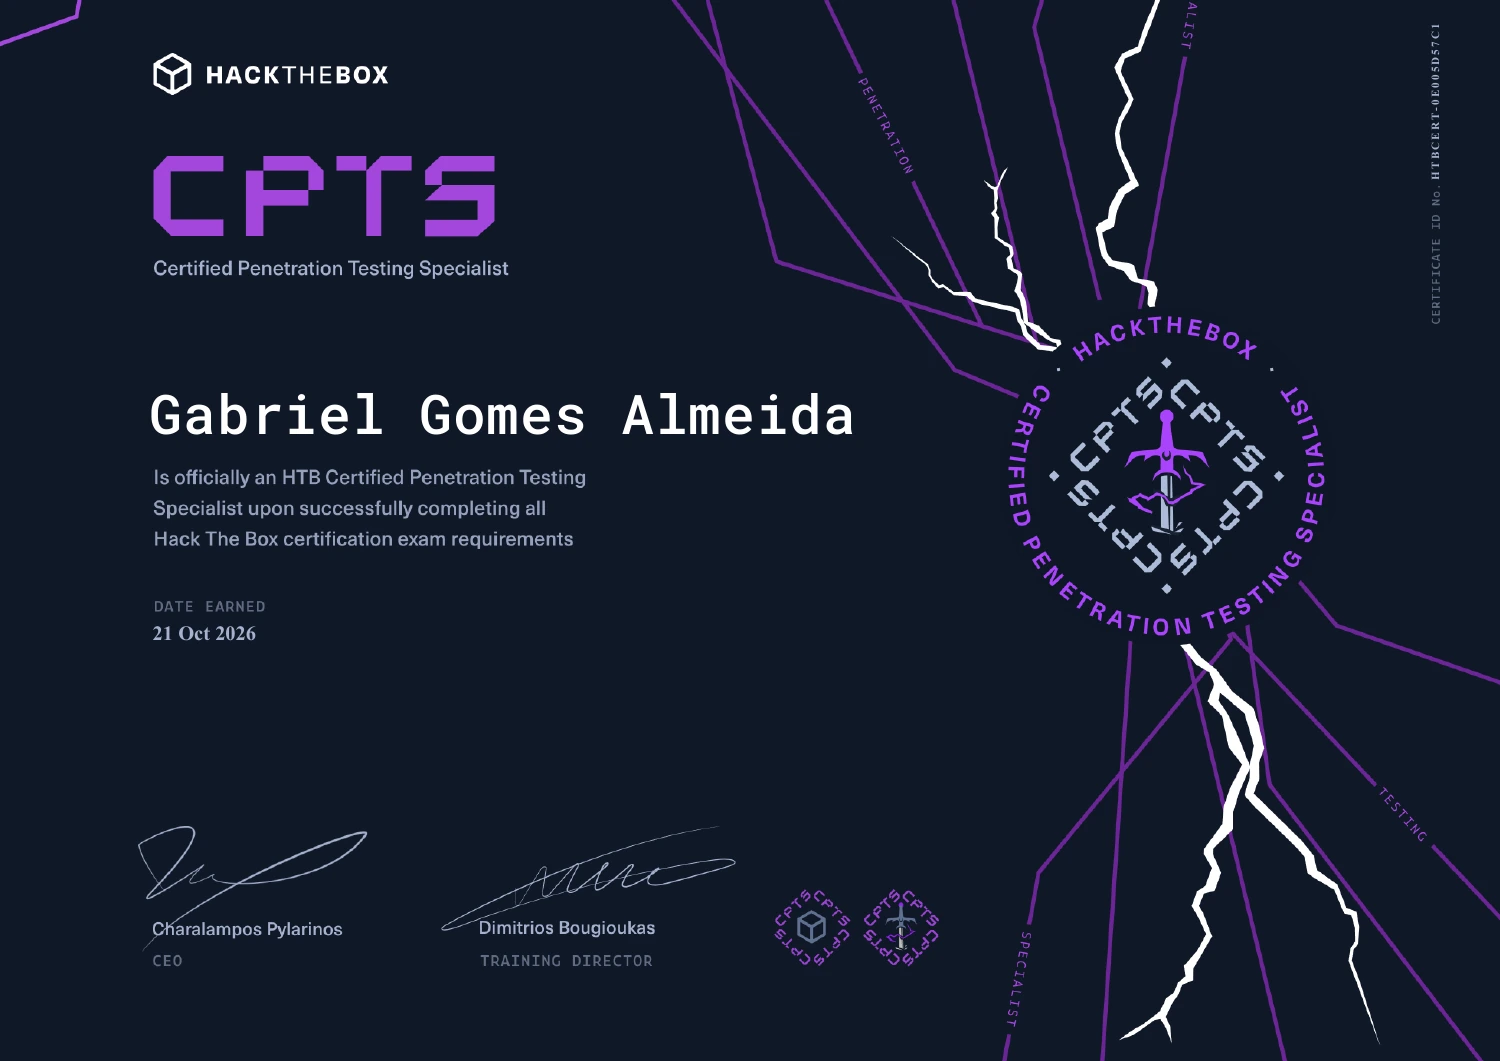
Gabriel Gomes Almeida’s original CPTS certificate, issued by Hack The Box on 21 October 2026 Open original certificate

Professional credential

Holder
Gabriel Gomes Almeida
Date earned
Certificate ID
HTBCERT-0E005D57C1
Download certificate Verify with Hack The Box

Look up the certificate ID and name in the official HTB portal.

OCI AI Foundations Associate

Oracle · 2025. Certification in artificial intelligence foundations.

Authorized labs

Practice in controlled environments to reinforce enumeration, validation, and documentation.

Systems Analysis and Development

Centro Universitário IESB · Brasília. Studies in systems, networks, databases, software engineering, and automation.

02 / Vulnerability research

Real findings. Public recognition.

Two CVEs published in open source AI projects, with researcher credit in official advisories. Research focused on authentication, authorization, and business logic.

CVE-2026-72917Moderate · CVSS 5.9

AnythingLLM

Account recovery security

An input-validation flaw weakened the requirement for two distinct account recovery codes. The finding contributed to fixing an important authentication safeguard.

CWE-180CWE-287Authentication
Research focus

Input validation and integrity of the account recovery flow.

Public credit: GabrielGomesAL · Reporter
Read official advisory — CVE-2026-72917
CVE-2026-70483Low · CVSS 3.1

Open WebUI

Isolation between users

A missing authorization check allowed a user to interrupt another user’s active response generation. The report contributed to strengthening access control in a multi-user environment.

CWE-862AuthorizationAccess Control
Research focus

Access control and isolation of operations between users.

Public credit: GabrielGomesAL · Reporter
Read official advisory — CVE-2026-70483

03 / How I work

Understand the code. Investigate the risk. Communicate the solution.

My background connects software development, automation, and vulnerability research. With experience at TJDFT and RP Prospecção, I bring a developer’s perspective to authentication, authorization, and application security.

01

Reconnaissance and enumeration

Mapping services, technologies, ports, routes, and technical clues before any validation.

02

Web, APIs, and applications

Reading flows, authentication, authorization, inputs, data exposure, and common application risks.

03

Linux, networks, and systems

Practical foundation in terminal usage, TCP/IP, Linux environments, versioning, automation, and behavior analysis.

04

Reporting and prioritization

Evidence, impact, safe reproduction, severity, and recommendations that help teams fix issues.

04 / Experience

Development, automation, and applied security.

My professional base comes from real systems, technical support, integrations, and process improvement, now directed toward offensive security and safer development.

TJDFT Jan 2025 · Jun 2026

Developer · Internship

Development and maintenance of internal systems, institutional portals, and dashboards. Platform integration, infrastructure support, and routine automation with Python, PowerShell, Bash, and n8n.

Internal systems Automation Technical support Applied security
RP Prospecção Jan 2024 · Jan 2025

Developer

Workflow automation with n8n and integration of systems, APIs, and databases. Technical support, troubleshooting, and improvement of internal processes.

Full stack Integrations Testing Documentation

05 / Projects

Code, practice, and problem solving.

Selected projects in development, networks, and automation. Explore the code and documentation in each repository.

Loading public repositories...

06 / Skills

From applications to infrastructure.

Recon and enumeration

Attack surface reading, ports, services, technologies, and validation paths.

Web and API pentest

Burp Suite, OWASP, authentication, authorization, and vulnerability analysis in web applications and APIs.

Linux and terminal

Linux environment, shell, permissions, processes, files, and lab routine.

Networks and TCP/IP

Networking fundamentals, services, protocols, diagnostics, and traffic interpretation.

Active Directory and Windows environments

Lab practice with Active Directory, BloodHound, and Impacket. Permission analysis and privilege escalation paths.

Python, PowerShell, and Bash

Scripts, routine automation, API integrations, and workflows with n8n.

Git, GitHub, and documentation

Versioning, repository organization, technical history, and clear documentation.

SQL, NoSQL, and analysis

Relational and non-relational databases, data reading, and support for technical investigation.

Power BI and visualization

Dashboards, indicators, scenario reading, and visual communication of data.

07 / Next step

Let’s build safer applications.

Seeking junior roles in penetration testing and application security, working remotely from Brazil. I bring CPTS certification, publicly credited research, and experience in development and automation to the team.

ggoalmeidaa@gmail.com